fringe963@gmail.com
2026-09-29 10:08
Mobile App Penetration Testing
19 Views
2026-09-29 10:08
ចង់ប្តូរការងារ ឬ កំពុងស្វែងរកការងារ ផ្វើសារឥឡូវនេះ
A mobile app ships to the attacker's device. They control the operating system, the network path and the runtime, which invalidates assumptions that hold perfectly well on a server. Our testing starts from that position rather than treating the handset as trusted.
Most serious mobile findings are not in the app at all — they are in the API the app talks to, which was built assuming only the app would ever call it. We test authorisation on every endpoint the binary reveals, including endpoints the interface never exercises, because an attacker calls them directly.
Manual mobile application penetration testing for native iOS and Android apps: binary analysis, local storage, transport security and the API layer behind the app.
Reference:
https://www.wimd.in/mobile-application-penetration-testing.html
អត្ថបទណែនាំ
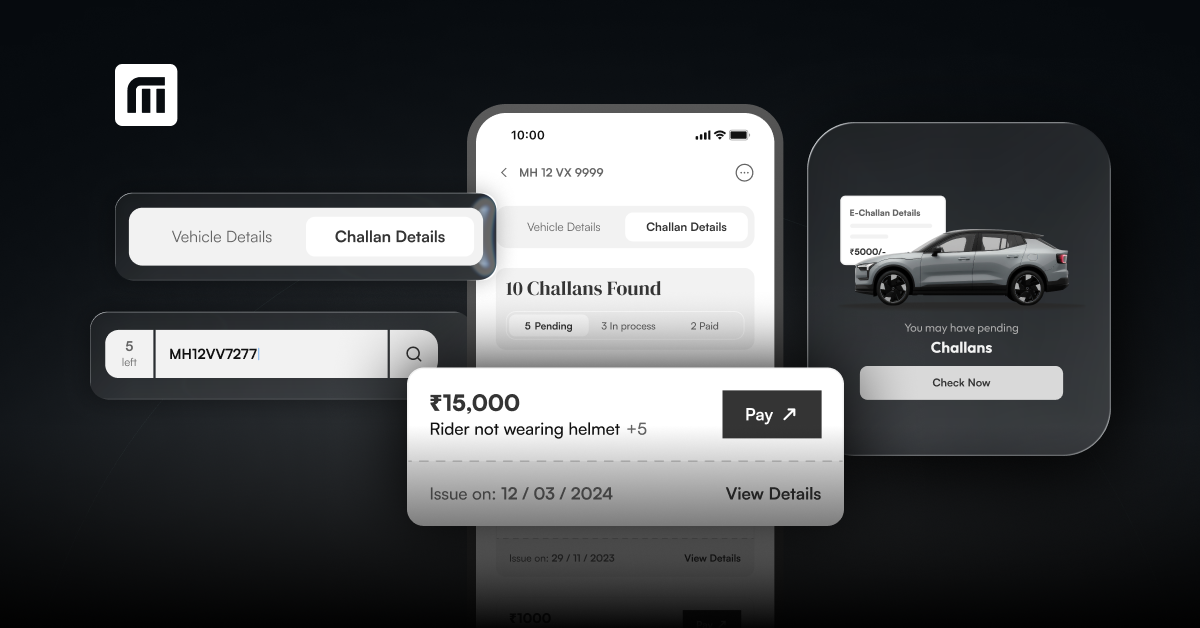
Vehicle RC, Challan, Insurance & PUC Check Online in India: The Complete 2026 Guide
ដោយ : ketki@zoop.energy 6 days ago
អត្ថបទថ្មីៗទាក់ទងបទពិសោធន៍ផ្សេងៗ
ដោយ : ketki@zoop.energy 1 day ago
ម៉ាស៊ីនបោះពុម្ព Print អត់ចេញក្រដាស - Can’t print: Troubleshooting steps
ដោយ : Pich Yorn 5 months ago
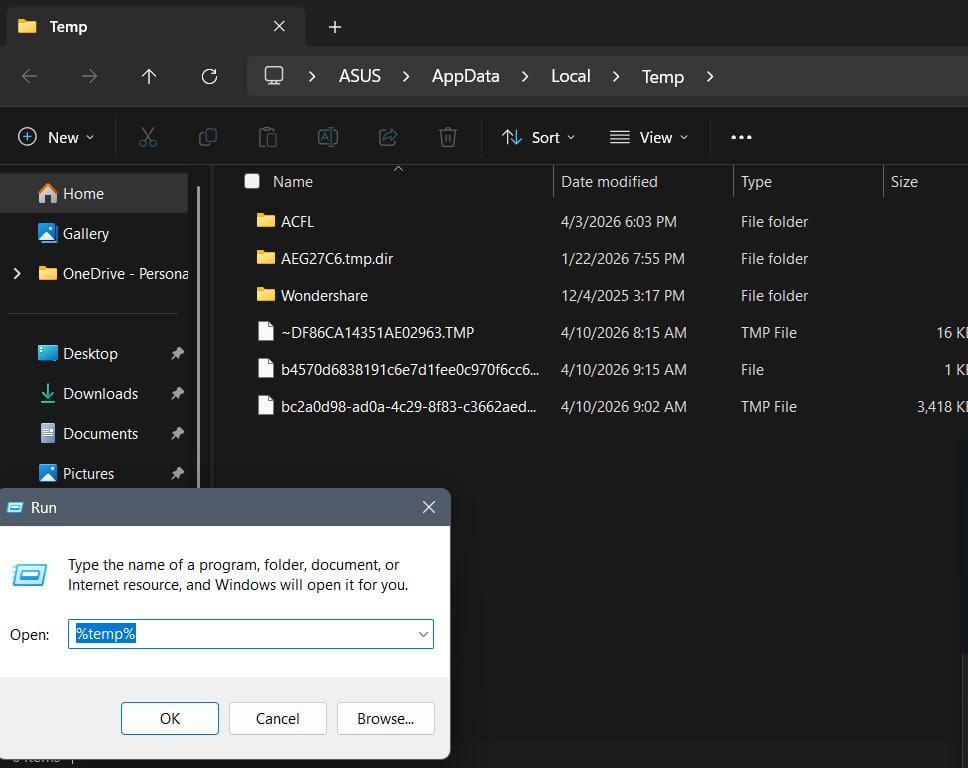
របៀបសំអាត file មិនសំខាន់ៗនៅក្នុង computer - Clean computer temp
ដោយ : Pich Yorn 5 months ago